wp2shell is already being exploited

kao

On 17-Jul-2026 an obscure security outfit Searchlight Cyber published their discovery: wp2shell - remote code execution in recent WordPress versions. Of course it was on Friday, the best time to publish information about an extremely dangerous bug! 😡

Since my blog runs on WordPress, I decided to analyze my webserver logs and see what's happening in the wild.

Read More →

Another update to Enigma Virtual Box unpacker

kao

Enigma Virtual Box authors made some changes in version 10.70 and broke my unpacker again. 🙁 To be able to support more and more versions, my unpacker requires some serious redesign.
That will take some thinking time and energy but I'll eventually get around to it.

In the meantime, here's a quick fix:

  • Detects and unpacks Enigma Virtual Box versions 10.70 and 10.80;

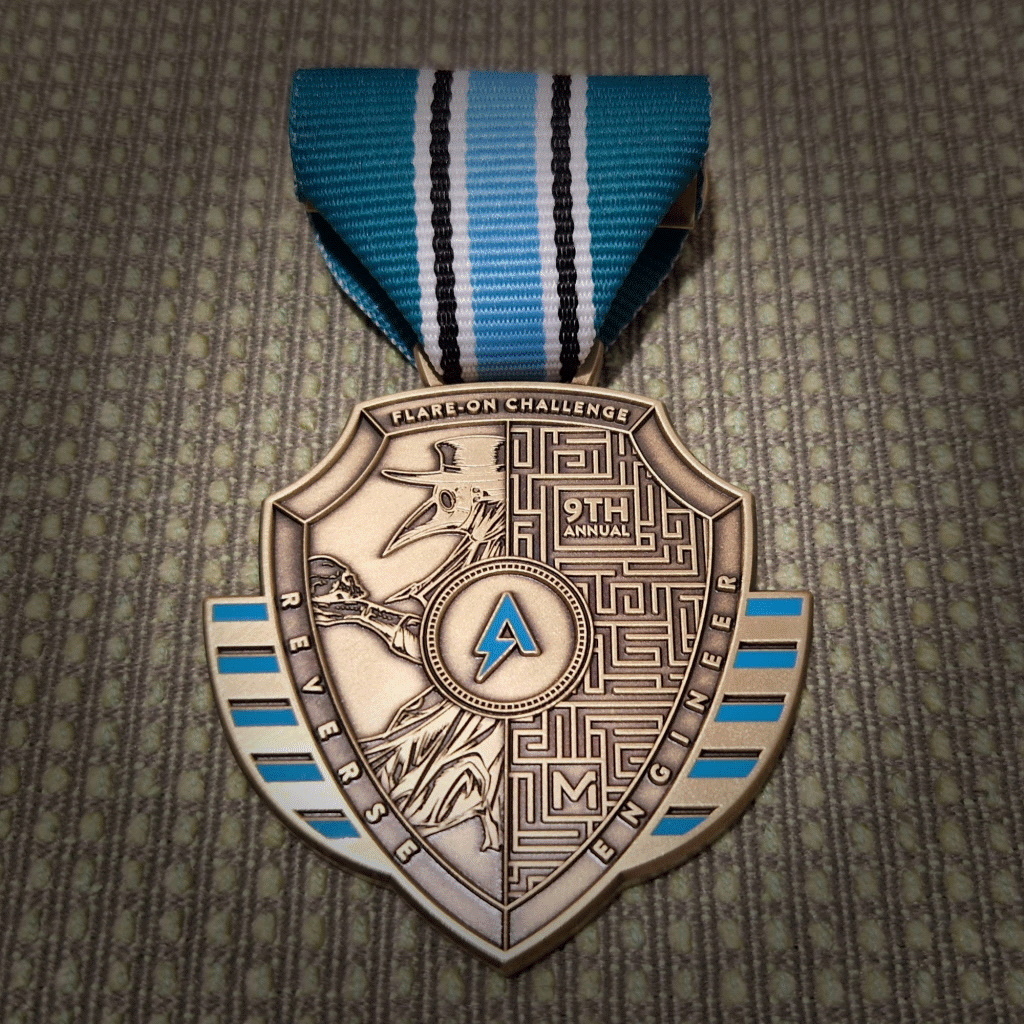
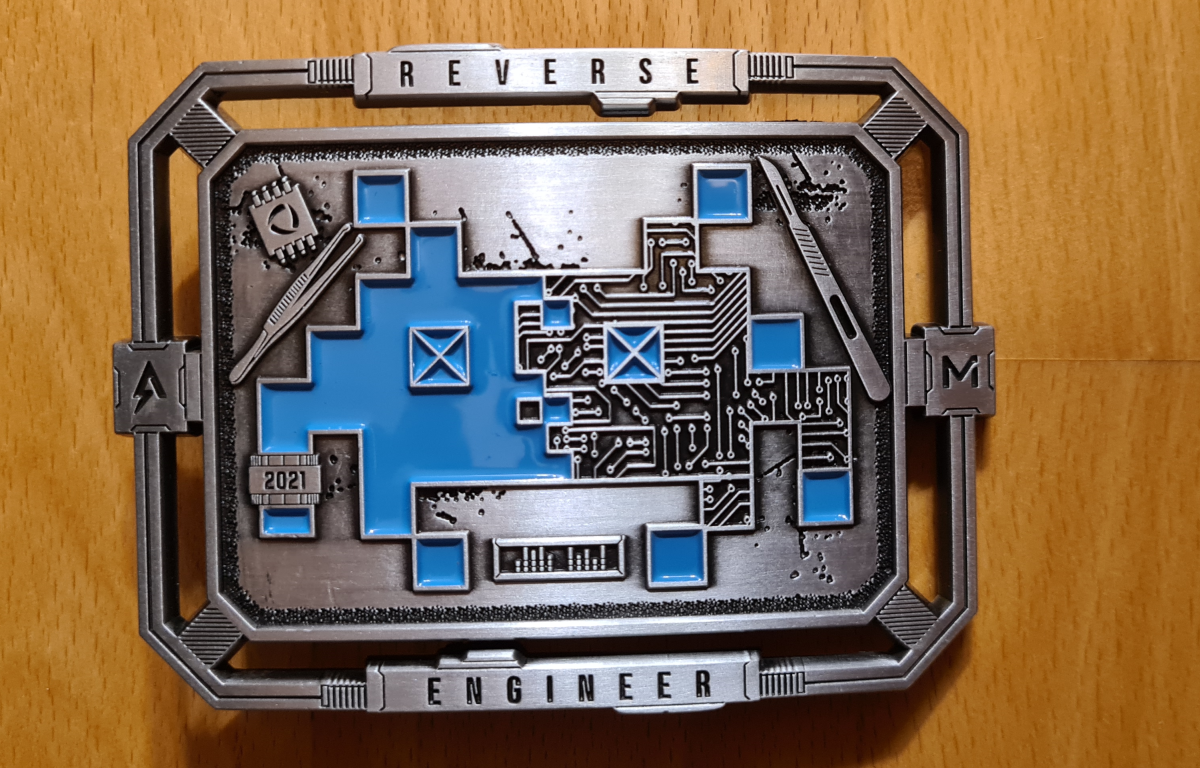
Flare-On 9 medal has arrived!

kao

It's taken over a year but the medal for 2022 contest is finally in my hands. 🙂

This time organizers had to deal with some manufacturing issues (which took them a full year to resolve), and I had to deal with overly zealous customs and taxes office. They billed me around 20 eur in taxes and surcharges for a simple trinket. Un-fucking-believable!

How security plugins for Autoplay Media Studio fail, pt.2

kao

Few weeks ago I wrote an article about misunderstood security in Autoplay Media Studio plugins. Two days later, author of DCrypto plugin released an updated version of the plugin. And just recently, he started to sell his plugin by making some pretty bold claims:

I present to you DCrypto with an advanced encryption that allows you to obfuscate your LUA 1.5 code in 256 Bit encryption with one of the best encryptions on the market, in addition to optimizing your source code, it will be protected with super protection.

Let's see how super this protection really is! 🙂
Read More →

How security plugins for Autoplay Media Studio fail

kao

Every once in a while I encounter a strange anti-reverse engineering protection. Protection authors are so focused on improving one specific aspect of the protection that completely overlook other, much easier ways how the system can be defeated.

Their logic is like this - someone stole my code, I better protect it. I've heard that cryptography is good, so I'll use that. Oh no, someone stole my code again! Let me add another layer of encryption over it! Few days/weeks/months later - Those bloody hackers won't stop! Let me protect my encryption code with another encryption!

Facepalm.

What the authors should do instead is stop and think. What do I want to protect? Against whom? For how long? What kind of loss is acceptable to me?

Read More →